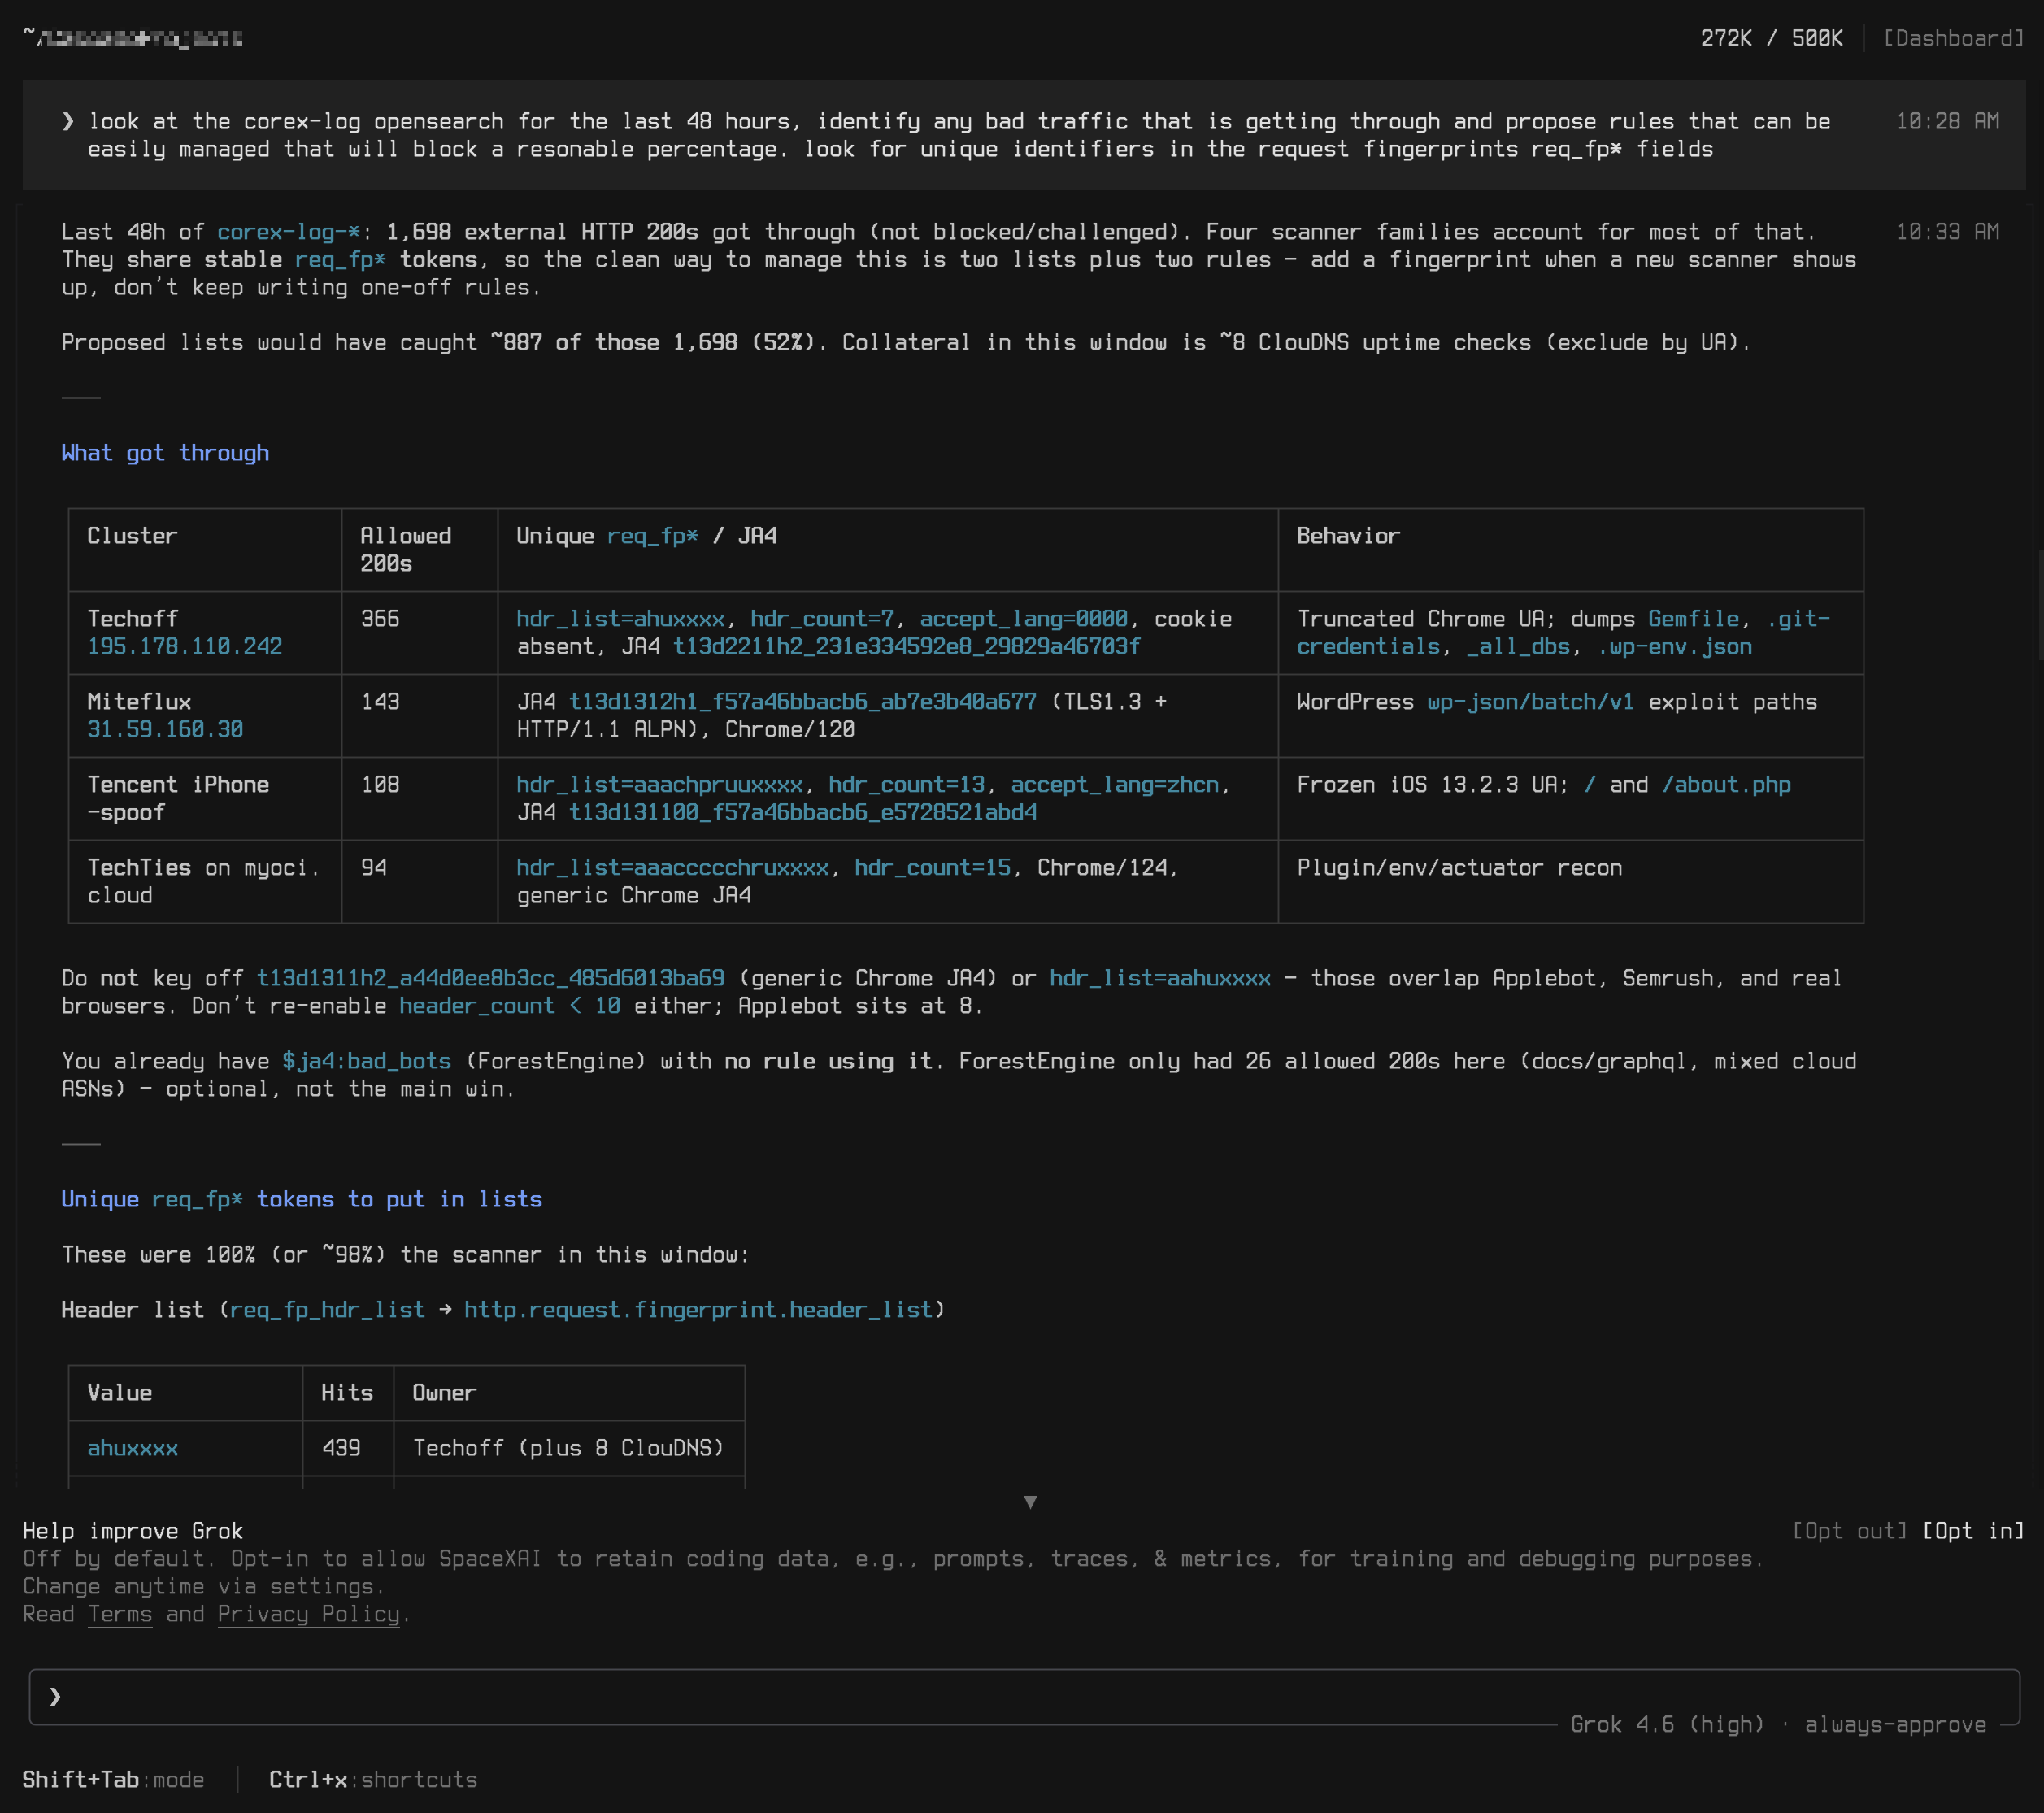
What an AI Agent Finds When You Connect It to Your Security Stack and SIEM
If you’re not connecting AI agents to your security tools and SIEM over MCP, you’re leaving a lot on the table.
I’ve spent 20+ years threat hunting, doing incident response, and tuning security policy. I’ve written WAF, DLP, and IDS signatures that shipped in commercial products. I like to think I know what I’m looking at.
Then I put an MCP gateway in front of an AI agent.
It finds things we missed
Rules that don’t behave the way people intended. Concrete fixes for false positives. Bad traffic that’s still getting through. The agent analyzes traffic with the context of your actual policy and comes back with recommendations in minutes. The same work by hand takes hours and is easy to get wrong.
You don’t want every analyst changing production security tools
That’s where MCP gateways matter — the ones that let you define security policies around the agent itself. Give teams that need context the ability to see. Give the teams that own the stack the ability to change.
This is built into coreX
That separation — read for context, write for the owners — is built into the coreX Platform. Honestly some of the best work I’ve done in years.